System of record for AI use
Govern every AI use.
Prove it when asked.
Inventory each use case, score the risk, take a human decision that is not the requester’s, and keep the evidence. Mapped to NIST AI RMF, ISO/IEC 42001, and the EU AI Act — as coverage, not a certificate.
No credit card. Or open a populated demo — no signup.
Schema isolation
Each organization in its own Postgres schema.
Separation of duties
The requester cannot approve their own use.
Four frameworks
NIST, ISO 42001, EU AI Act, OECD — mapped, not certified.
Audit package
Register, decisions, evidence index, history.
Move fast on AI — without losing the record.
Ungoverned AI is a board-level risk: privacy exposure, biased decisions, and no answer when an auditor asks how it is controlled. This is the register those answers come from.
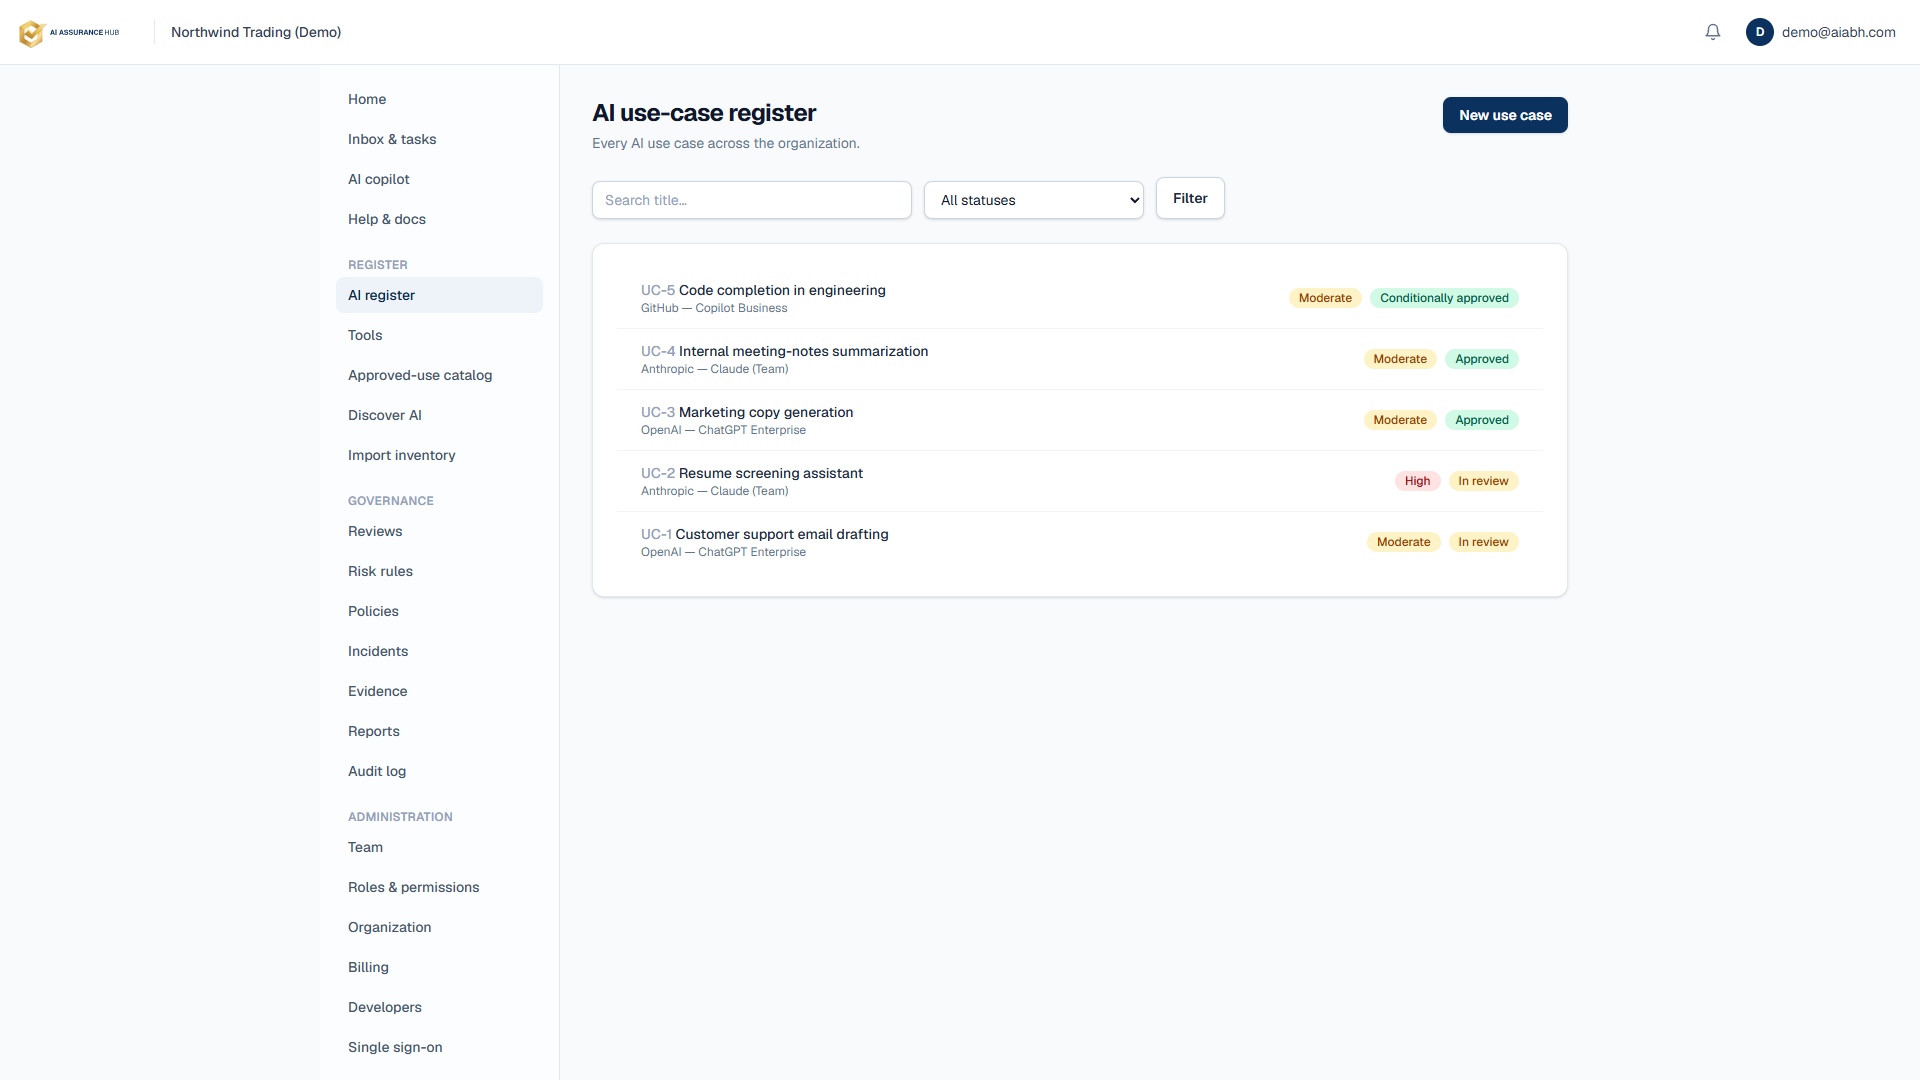
See every use of AI
Inventory the AI tools and use cases across every team — including the shadow AI already in use — in one structured register.
Control the risk
Score each use case against explainable risk rules, then route it for human review, approval, and safeguards — before it ships.
Prove it on demand
Generate audit-ready exports and live framework coverage — evidence, decisions, and history your auditors and board can trust.
Could you answer these today?
01
Which AI systems are being used — and by whom?
02
What data and decisions does each one touch?
03
Who approved it, and on what basis?
04
What safeguards and evidence can you show an auditor?
The platform
Identify every use. Govern the risk. Prove it on demand.
Identify
One register for every AI use — not a folder of spreadsheets.
Tools, owners, data categories, automation level, and status in a single tenant-scoped register.
- Versioned records, searchable and role-scoped
- Shadow AI sits next to sanctioned uses, not in a side list
- Owners and human-oversight are required fields, not comments
Govern
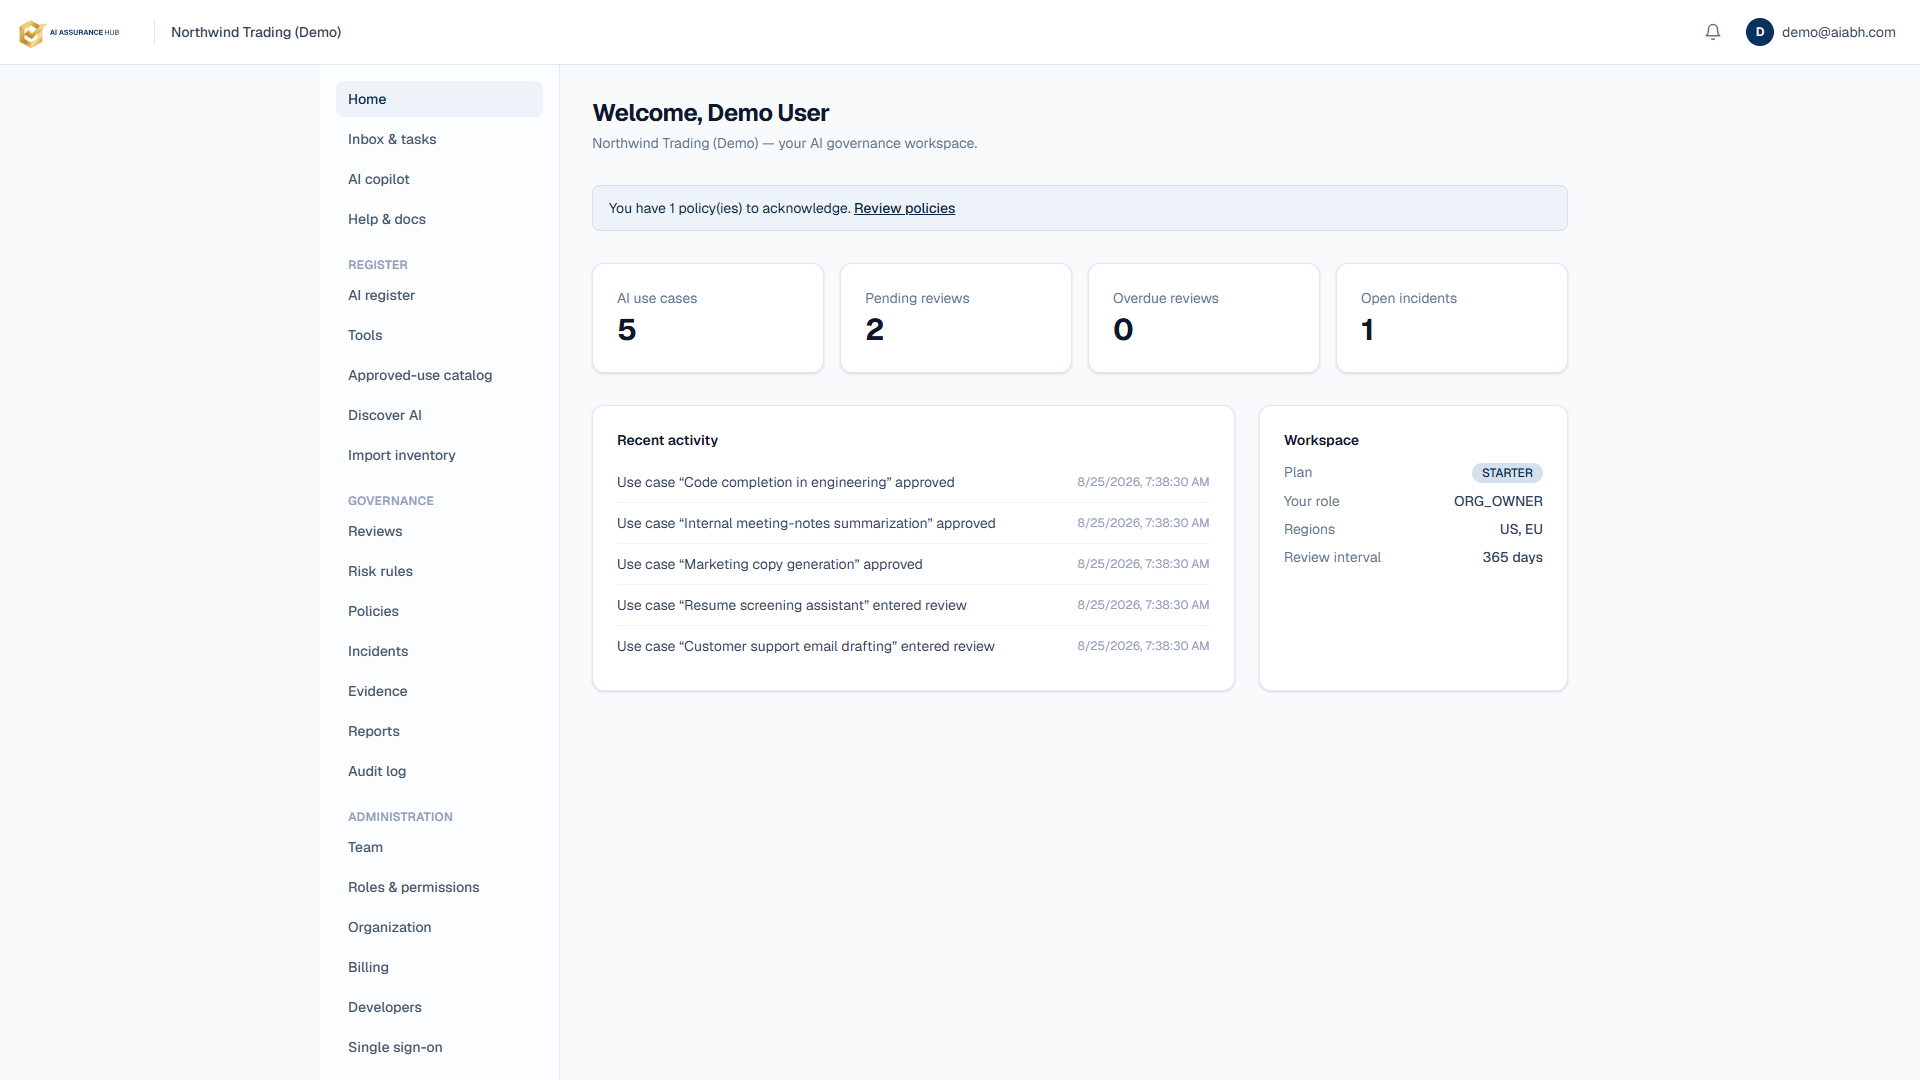
A live operating picture, not a quarterly slide.
Home shows what is in review, overdue, and open. Inbox is the work queue: decisions, acknowledgements, safeguards.
- The requester cannot approve their own use
- Risk tiers are deterministic, explainable, and snapshotted
- Conditional approvals attach safeguards with verification
Prove
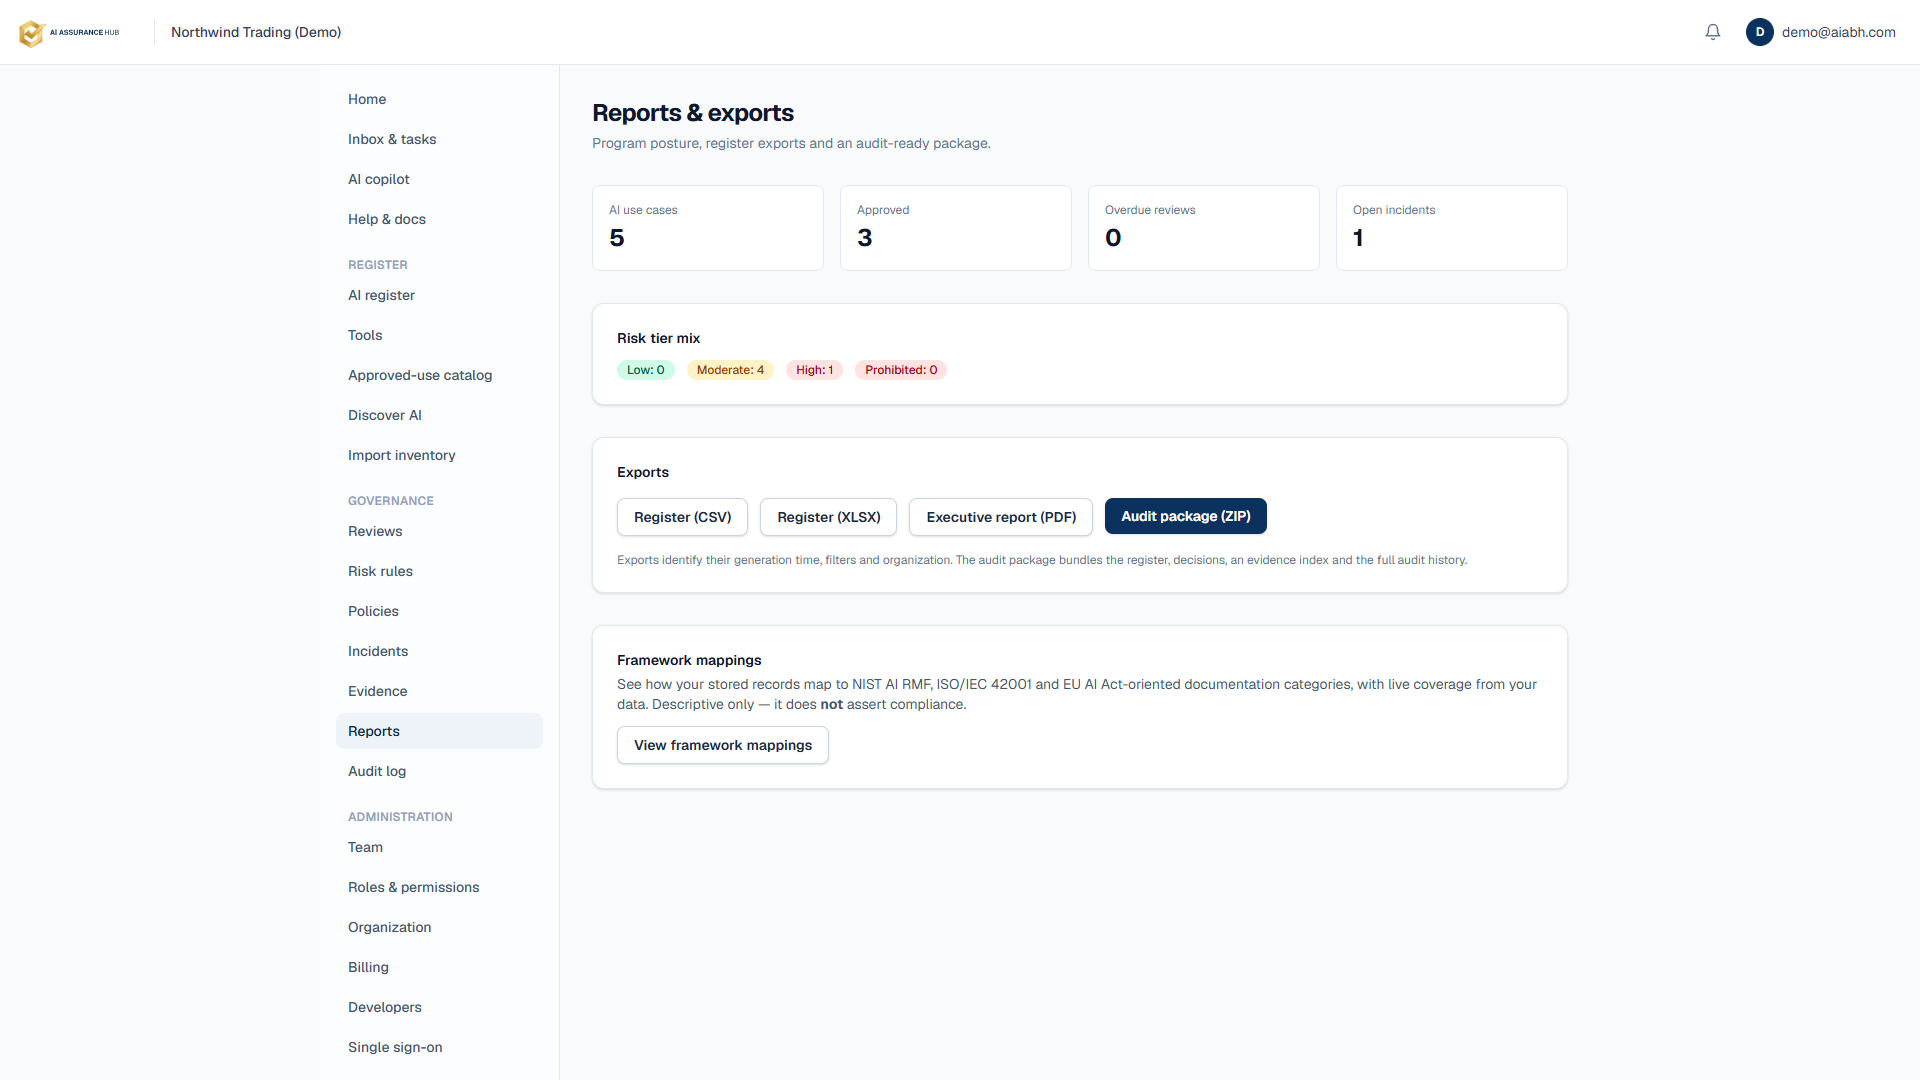
When someone asks, you export the package — you do not assemble it.
Register CSV/XLSX, executive PDF, and an audit ZIP. Framework coverage is live from your records.
- Decisions, evidence index, and append-only history in one ZIP
- Mapped to NIST AI RMF, ISO/IEC 42001, EU AI Act, OECD — as coverage, not a certificate
- Hand the package to an auditor without rebuilding a slide deck
What is in the system
One register. One decision. One package for the auditor.
Built as a system of record, not a GRC suite with AI bolted on.
- AI use register
- A single source of truth for tools, use cases, owners, data categories and human-oversight — versioned and role-scoped.
- Risk engine
- Versioned rule sets produce deterministic risk tiers with full explainability and immutable assessment snapshots.
- Governance workflow
- Reviewer queue, decision outcomes, conditional approvals, safeguards with verification, and periodic re-review.
- Policies & assurance
- Publish policies, capture acknowledgments, log incidents and exceptions, and store evidence with presigned access.
- Audit-ready reporting
- Register CSV/XLSX, executive PDF, and a complete audit-package ZIP — plus live framework coverage mapping.
- Built for scale
- Schema-per-tenant isolation, SSO/SAML + SCIM, a public REST API with signed webhooks, and platform admin controls.
Framework alignment
Show your work against the standards that matter.
Records map live to common AI governance frameworks — per-category coverage you can hand to auditors. Descriptive mapping, not a compliance claim.
NIST AI RMF
Govern · Map · Measure · Manage
ISO/IEC 42001
AI management system
EU AI Act-oriented
Documentation categories
OECD AI Principles
Values-based principles
For organizations
Give risk, legal and security a shared, controlled workflow — and give leadership a defensible answer whenever AI use is questioned.
- One governed register across every team
- Role-based approvals and separation of duties
- Audit-ready evidence in seconds
For consultants & MSPs
Run AI governance as a service. Manage many client organizations from one console, with full tenant isolation and branded reporting.
- Up to 25 client organizations per seat tier
- Reusable templates and cross-client dashboard
- Strict schema-per-tenant data isolation
Controls, not slogans
The controls serious buyers expect — already built in.
We’re onboarding our first design partners. Every workspace runs on the same security and governance foundations from the start.
- Schema-per-tenant data isolation
- SSO / SAML + SCIM provisioning
- MFA enforced for privileged roles
- Encryption in transit & at rest
- Append-only audit trail
- Mapped to NIST · ISO 42001 · EU AI Act
Pricing
Simple plans that scale with you.
Start free, upgrade when you’re ready. Every plan includes the register, approvals and audit trail.
Starter
Small teams standing up their first AI register.
$149 / month
- One organization
- Register, approvals & policies
- Standard exports
- Up to 10 users
Business
Growing companies that need full governance and reporting.
$399 / month
- Advanced risk rules
- Incidents, evidence & reporting
- Up to 50 users
Consultant / MSP
Consultants & MSPs governing AI for multiple clients.
From $499 / month
- Manage up to 25 client organizations
- Templates & cross-client dashboard
- Branded reports
Prices in USD, billed monthly. Every plan includes the register, approvals, and audit trail — cancel anytime. Prefer annual billing? Contact us for a discount.
FAQ
Questions, answered.
Does this make my organization compliant?
No platform makes you compliant on its own. AI Assurance Hub is the system of record that helps you run a credible governance program and evidence it. Our framework coverage is a descriptive mapping to standards like NIST AI RMF, ISO/IEC 42001, and the EU AI Act — not a legal determination.
How long does it take to get started?
Minutes. Create a workspace, adopt a framework-mapped policy template, and register your first AI use case — or load sample data to explore a fully populated register right away.
Is our data isolated from other customers?
Yes. Each customer's governed data lives in its own isolated database schema (schema-per-tenant), with no cross-tenant references by design. Access is role-based, privileged roles require MFA, and you can enforce SSO and IP allow-listing.
Do we need to be technical to use it?
No. It's built for risk, legal, security, and governance leads — a guided workflow to inventory, assess, approve, and evidence AI use. No code required.
Which frameworks does it map to?
Your records map live to NIST AI RMF, ISO/IEC 42001, EU AI Act-oriented documentation categories, and the OECD AI Principles, with per-category coverage you can hand to auditors and executives.
Are you SOC 2 certified?
SOC 2 is in progress. A SOC 2 report is issued by an independent auditor after an observation period; until then we do not claim certification. See our Trust & Security page for the controls we operate today.
Can consultants and MSPs manage multiple clients?
Yes. Run AI governance as a service — manage many client organizations from one console with strict tenant isolation, reusable templates, and white-labelable reporting.
Put your AI use on the record.
Stand up a governed AI register today and be audit-ready before your next board meeting.